- Does it support single sign-on and per-person permissions?
- Per-person permissions are built in: admin and user roles scoped per company and site, with a full audit trail on every action. Company-wide single sign-on (SSO) is on the enterprise roadmap; today, enterprise deployments use per-person logins with role-based permissions. Tell us your login system and we'll plan SSO with you.
- How do we roll it out across dozens of sites?
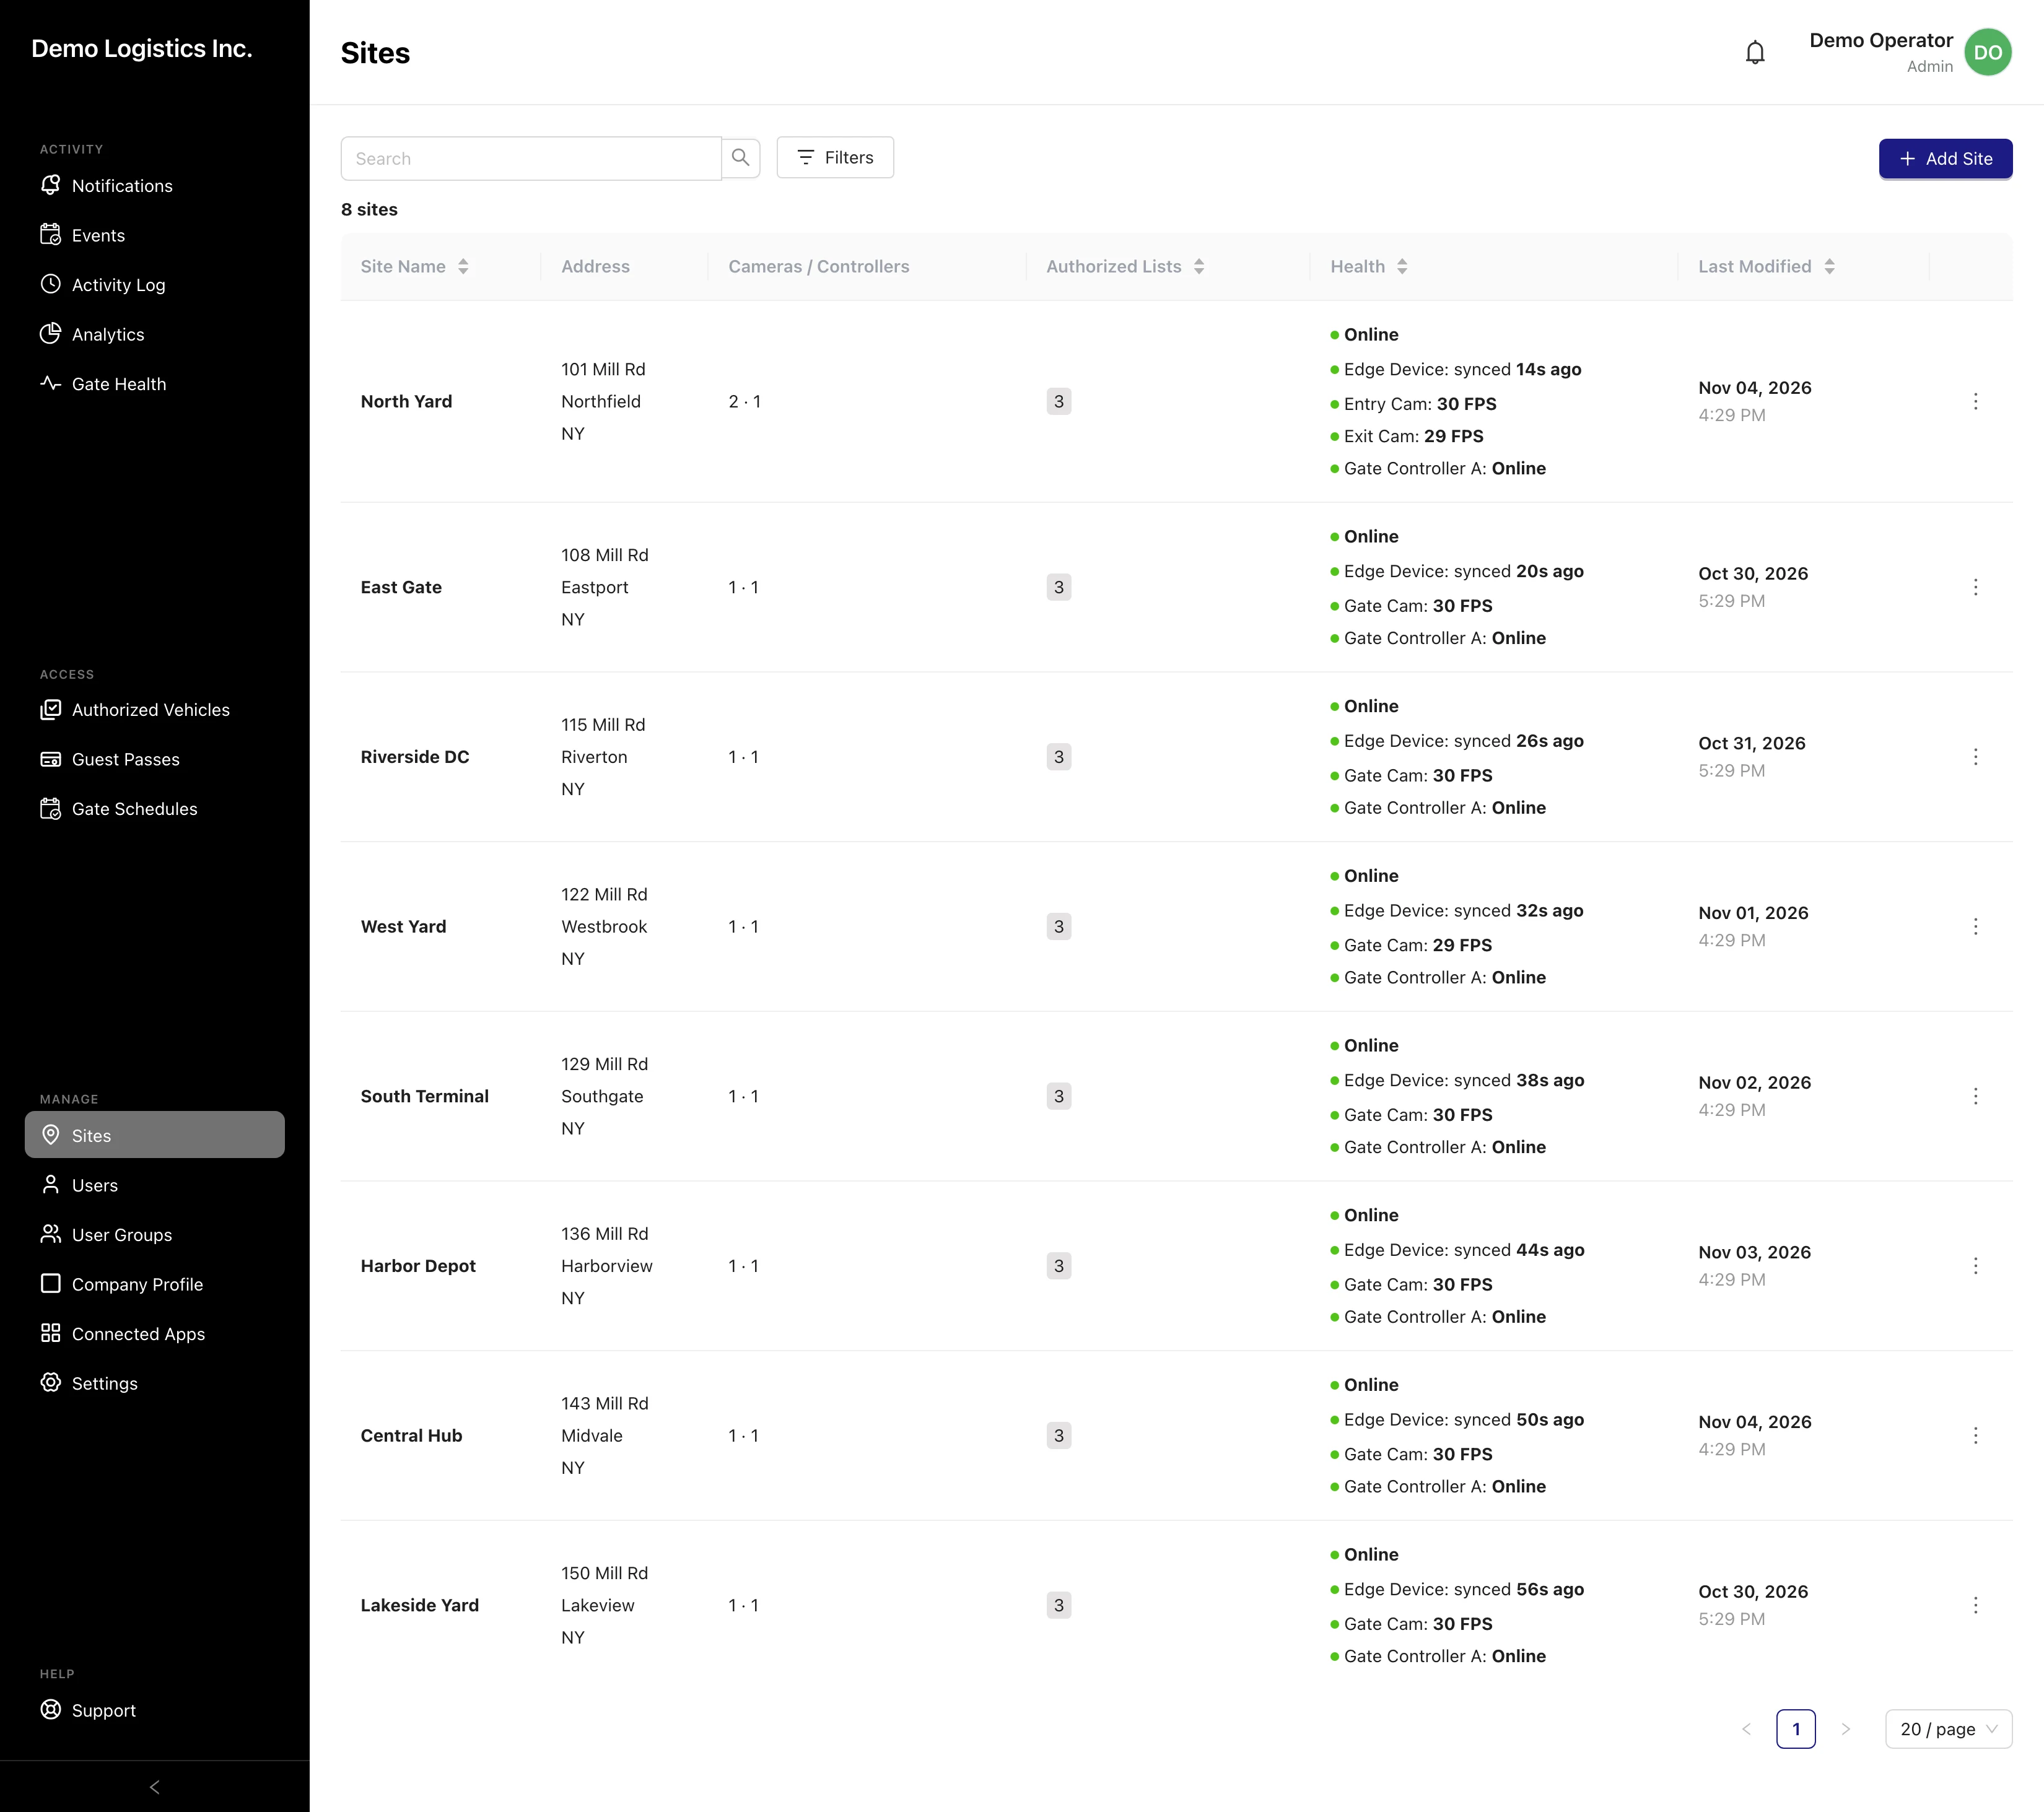
- Site by site, on the gates you already have, about half a day per gate, no rebuilds. Most portfolios pilot a few sites, lock a standard policy, then roll the rest out on that template, with remote support at every commissioning.
- Will it pass our security review?
- It's built for it: AES-256 at rest and TLS 1.2+ in transit, an NDAA-compliant camera, per-person logins with role-based permissions, and plate-reading that runs at the gate, so recognition and gate decisions never depend on the cloud. Access events sync to your dashboard over TLS 1.2+. We support your vendor security and compliance review with documentation and audit-ready exports.
- What happens at a site that loses internet?
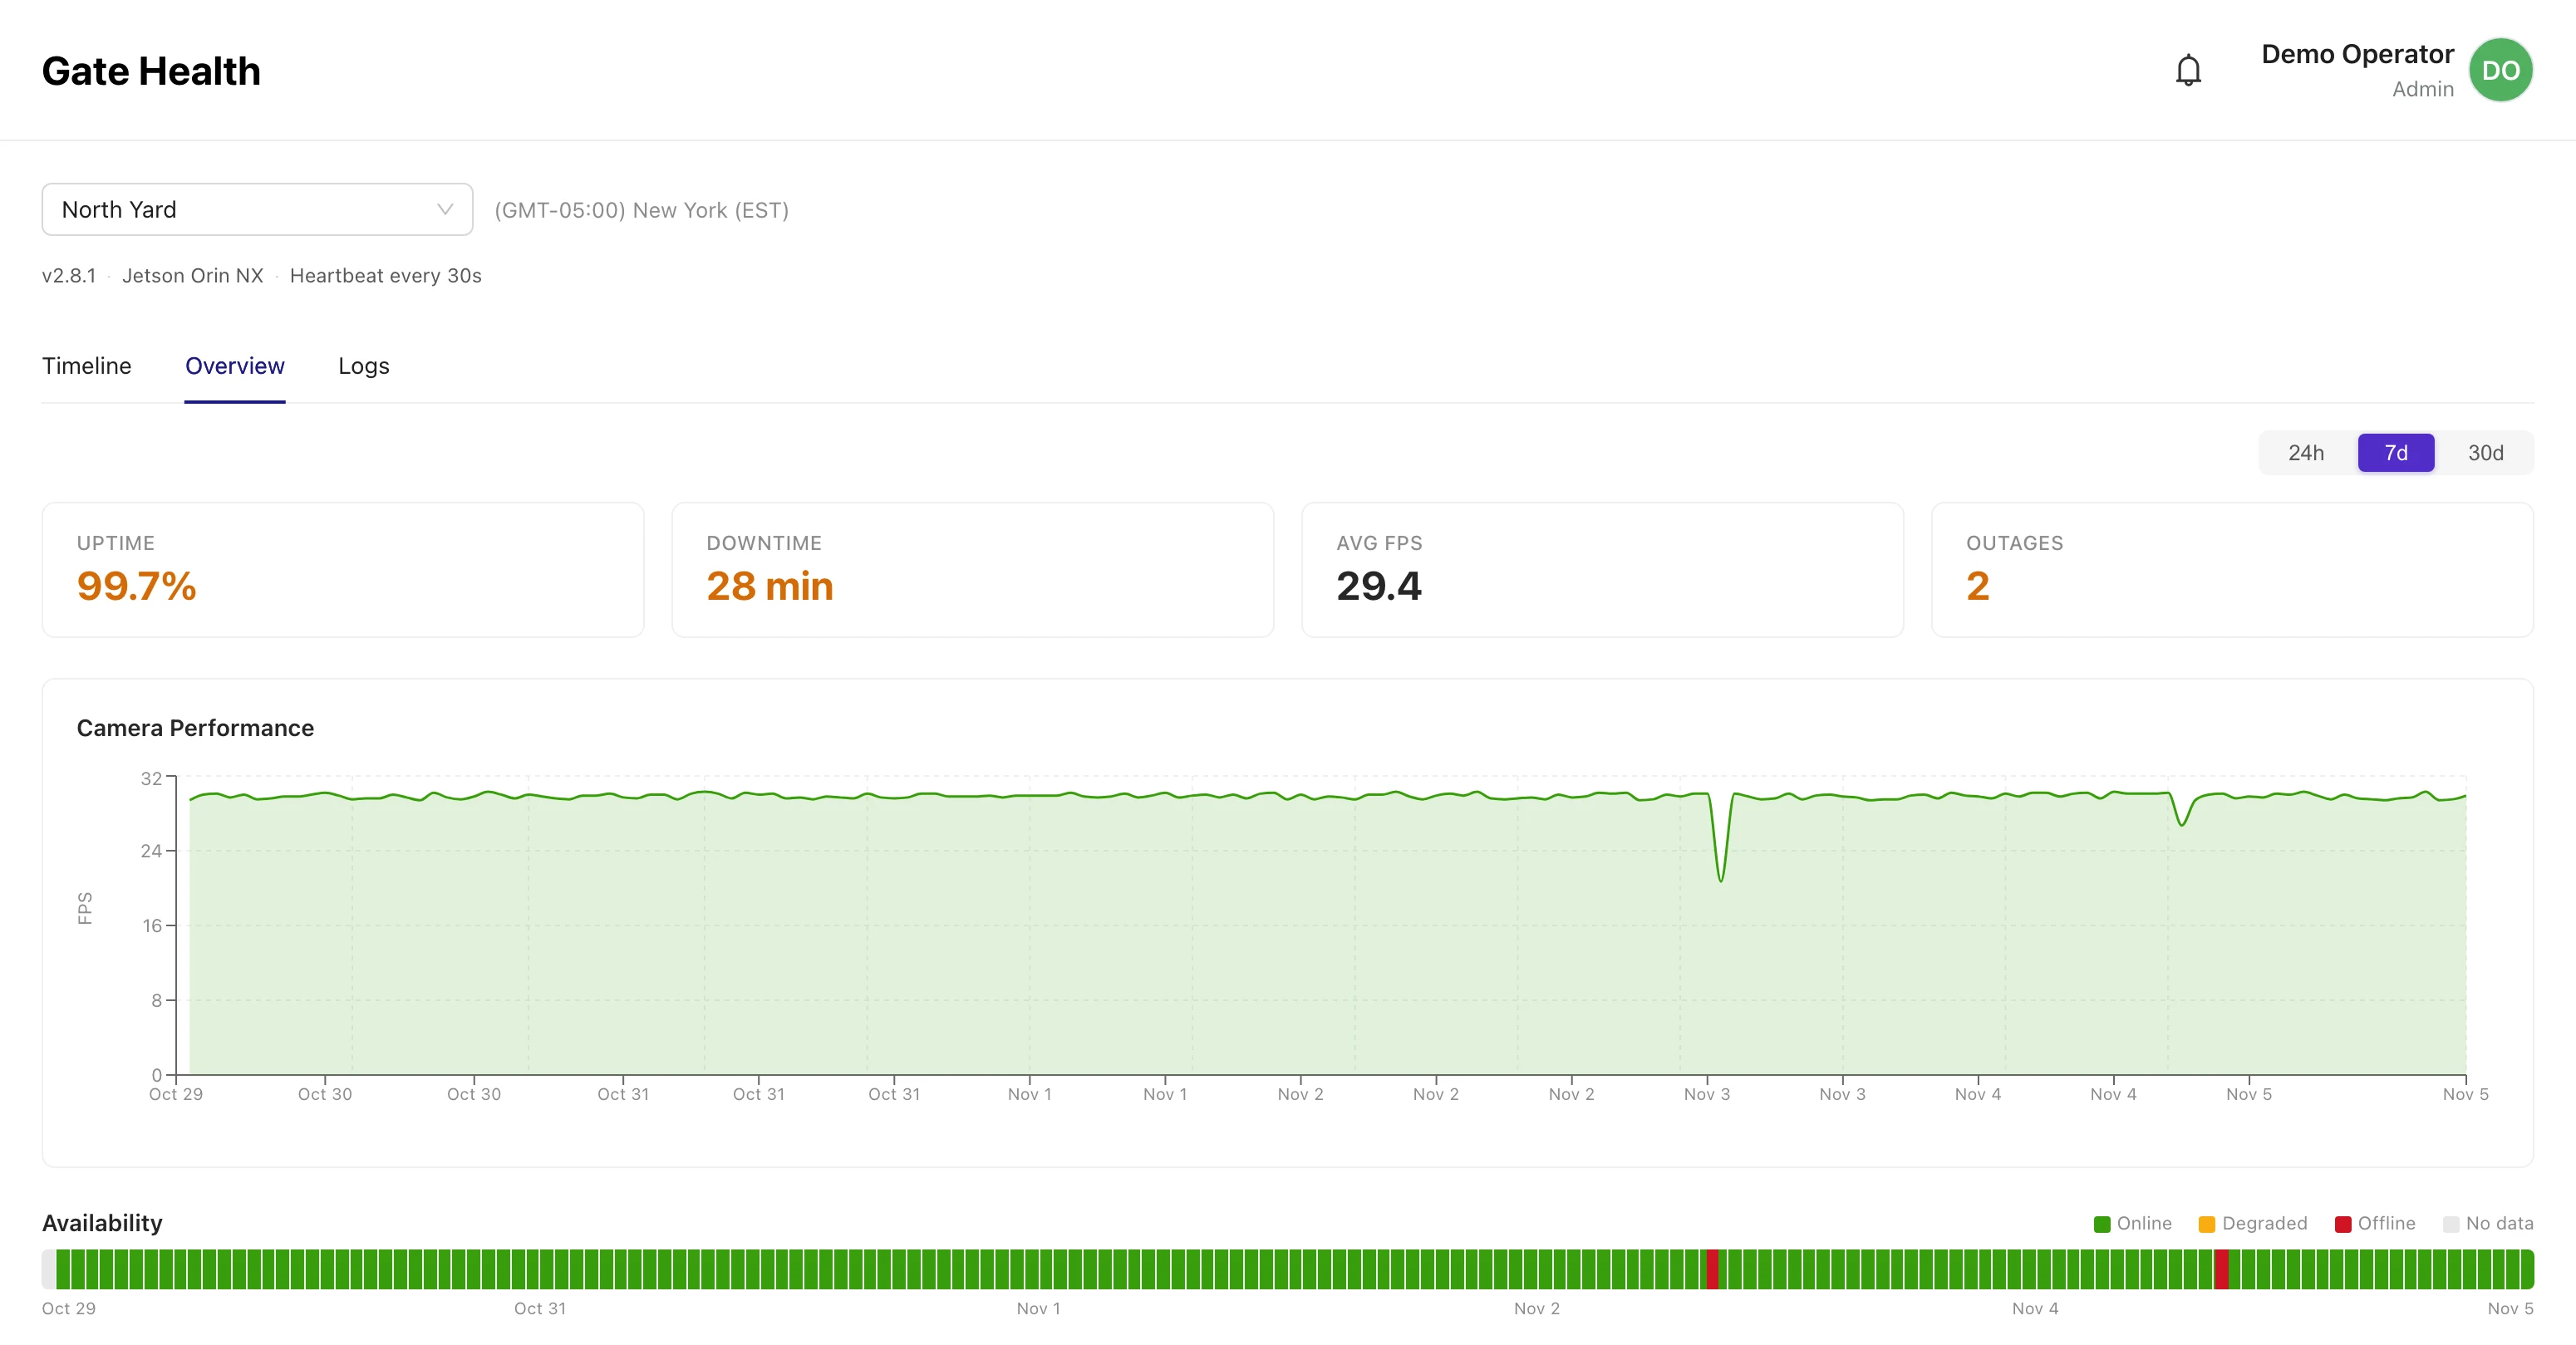
- Gates keep opening on the cached local access list (a site can run fully disconnected for up to 30 days), and every event syncs automatically when the connection returns. Recognition and gate control run on-site, not in the cloud. A network blip never strands a gate.
- How does it fit the systems we already run?
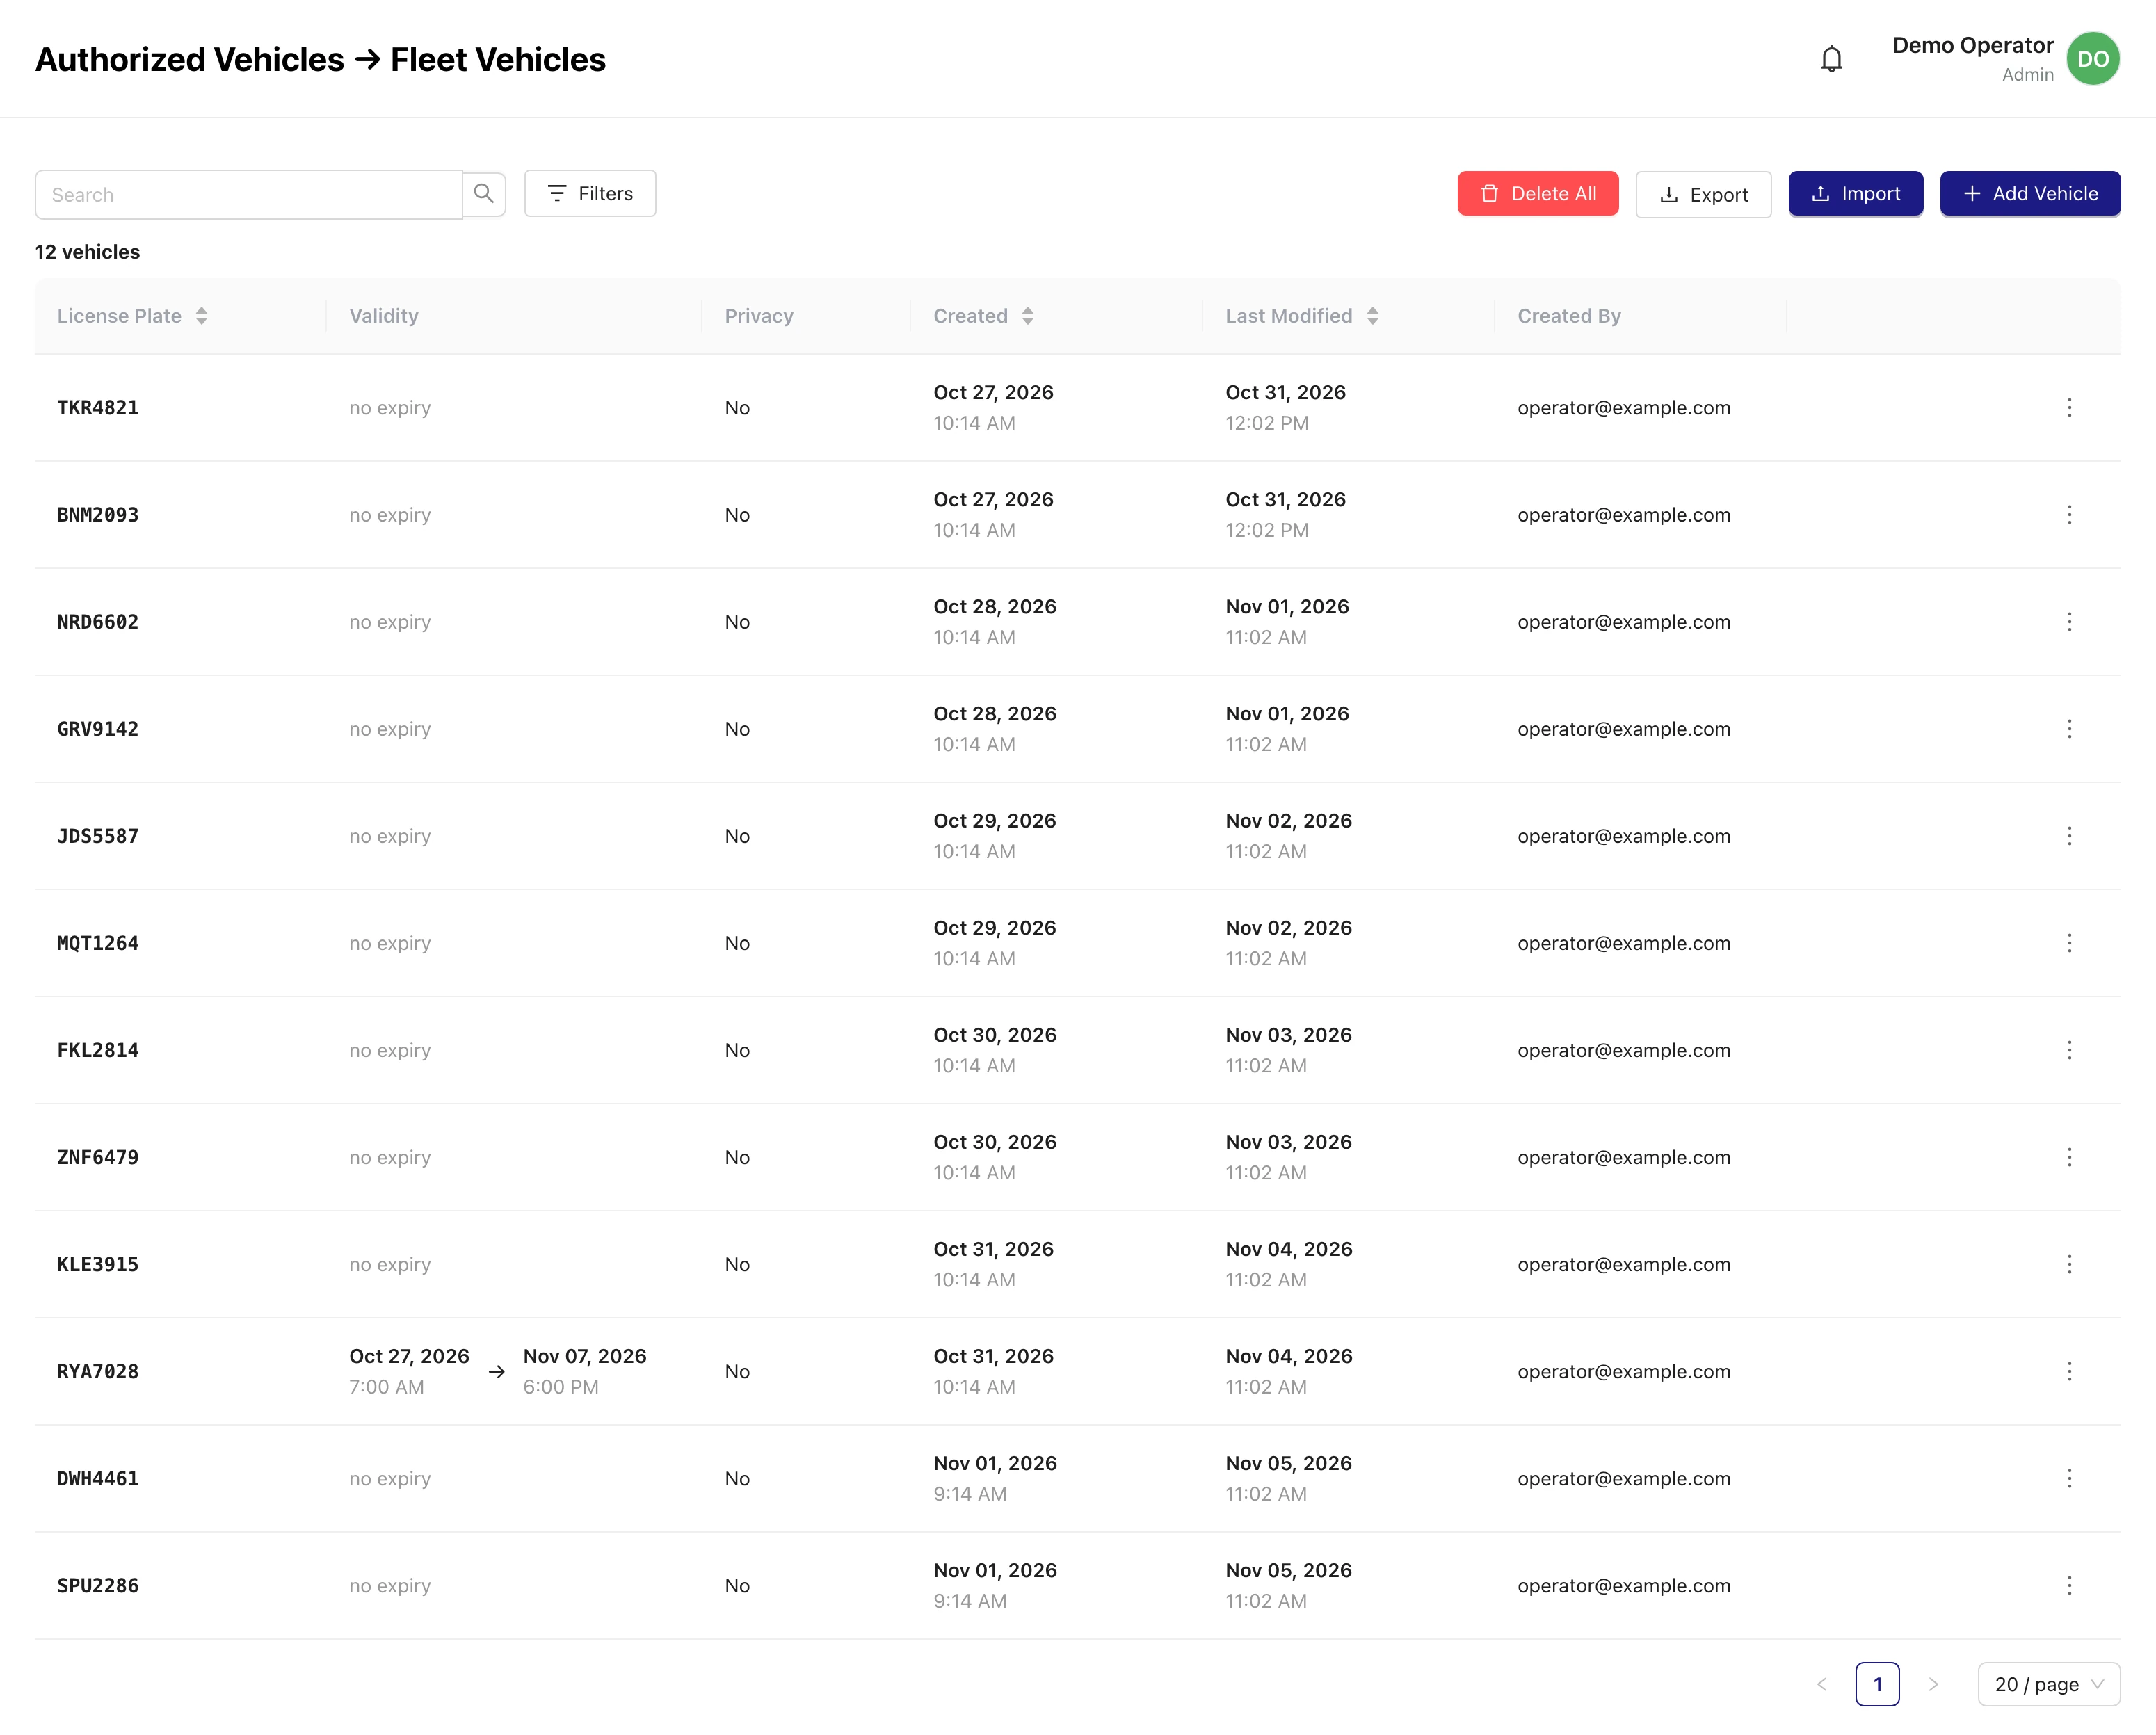
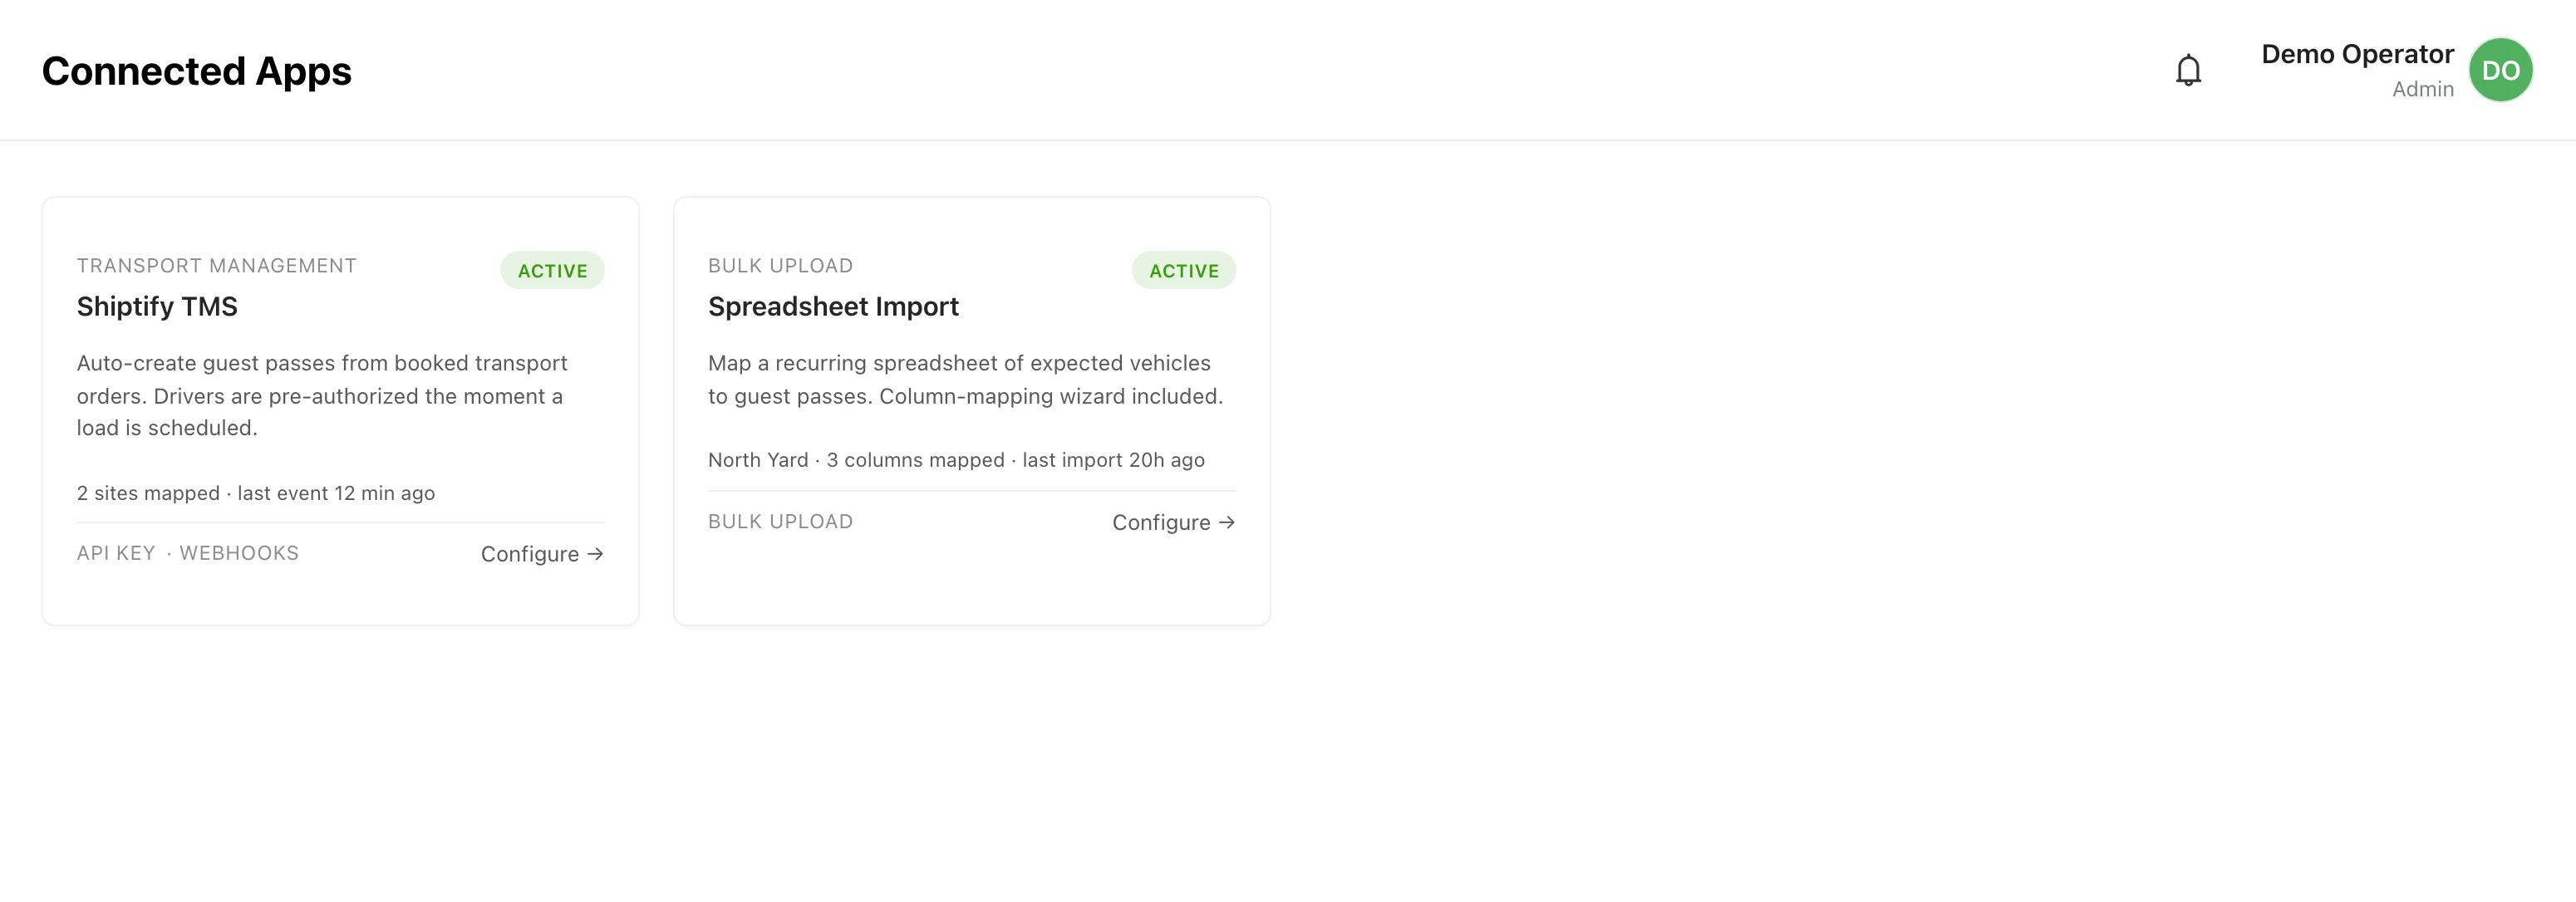
- It connects to your other software two ways: a full developer interface (API) for custom links, and a ready-made Shiptify connector and spreadsheet imports (more connectors in progress), so access stays in step with operations, with nothing entered twice. We share the full API reference during evaluation.
- Who manages it, and how is access governed?
- Your operations or security team, from one dashboard, central policy with per-site overrides, every change attributed and logged. No technical expertise required, and nothing happens at a gate that your rules didn't allow.